Knowledge base

October 28, 2026

Sensitive Information in AI Chat, Teams, and WhatsApp: The Moment Before Sending

When you think of a data breach, you think of a hacker. In reality, it often starts with Ctrl+V: a snippet from a file ending up in the wrong chat, the wrong email, or an AI tool that “tweaks” the text a bit.

There’s no malicious intent. There’s just a rush—and a button that’s too close at hand. This blog post is about that one moment right before you hit send: what can you still do to stop it, and who will notice?

Where Microsoft 365 Ends

In the blog post about Microsoft Purview, you saw what Business Premium already protects: email and files in OneDrive and SharePoint. A file you share in Teams is also included.

Not the chat message in Teams. According to Microsoft, DLP for Teams chat requires an E5 license. And Microsoft doesn’t detect AI chat in the browser or an app on a laptop at all.

AI Chat and Confidentiality

An employee pastes a letter to a client into a free AI chat—using his personal account—to help him word it better. The client’s name, address, and the reason for the case are included and sent to a service with which your organization has no data processing agreement.

Bans don’t work well. The tool remains useful, and those who aren’t allowed to use it will use it secretly. A better approach: find out which AI tools your team is using, and agree on what’s allowed for each tool.

WhatsApp is not a file

The community nurse sends a photo to the colleague who is taking over the shift. The technician texts the customer a quote with the customer’s address. It’s quick, and it’s often done on a personal phone.

This means that business data is stored on a device that the organization does not manage, in an app that it cannot archive. If the employee leaves, the conversations go with them. Any alternative must be just as fast; otherwise, no one will use it.

A warning at just the right moment

You’ll forget a training session on data breaches in a week. But you won’t forget a notification that appears the moment you send an email. In Outlook, Microsoft 365 already does this: if an email contains sensitive information, a notification appears at the top of the screen before the email is sent. For chat and for apps outside of Microsoft, you’ll need software installed on your device to enable this feature.

Protect without spying

Any form of data breach prevention raises one question for employees and the works council: Is the employer monitoring our communications? Ask yourself that question before you make a decision. A single report per type of data is enough to prevent a breach. Names and message content are not necessary for this.

Start with an AI overview

You don’t have to start with software. Start by making a list of the AI tools your team uses, what they’re used for, and what data they process. Often, the list will include tools that no one expected.

The European AI Regulation requires providers to label AI output. Since August, they have been required to label what their AI generates in a machine-readable format; for tools that were already on the market, the transition period runs until December 2. That is their obligation. Your job is to know what you’re using.

The AI Registry does not provide a legal opinion. However, in about ten minutes, it generates an overview of your AI tools, including the transparency statements, and sends it to you as three documents via email.

This Is How We Do It

We’ll start with the AI overview and the specifications for each tool. Next, we’ll enable Purview for email and files. We’ll address the gaps outside of Microsoft with on-device data breach prevention, as an add-on to the modern workplace. We operate in accordance with ISO 27001:2023, ISO 9001:2015, and NEN 7510:2024.

Frequently Asked Questions

Can an employee use an AI chatbot for work?

You decide that yourself, on a per-tool basis. Specify which tools are allowed and what data should not be included in them. A business subscription with a data processing agreement is different from a free version with a personal account.

Does Business Premium protect Teams?

Files you share in Teams are included, since they’re stored in SharePoint or OneDrive. The chat message itself isn’t; for that, Microsoft requires E5.

Do I need to label AI output myself?

It is the AI tool provider’s responsibility to label AI output. What matters for you is that you know which tools you’re using and what you’re inputting into them.

Conclusion

A data breach usually starts with a patch, not a hacker. Microsoft 365 protects email and files; the chat feature, the AI tool, and the app on your laptop are not covered. Start by getting an overview of what your team uses, and agree on what’s allowed for each tool.

Would you like to discuss this before sending it? Schedule a meeting with ALTA-ICT.

Want to know more?
Get in touch
/
Hero Voor Verzenden.html
HTML

maak synccommanodo

Je stuurde de HTML-bron, niet de PNG. Ik heb die HTML zelf gerenderd en het resultaat bekeken. Het beeld is akkoord.

Wat ik heb gecontroleerd

Maat en fonts: exact 1200x900. Halogen 900 en Bilo 300 en 500 laden uit het bestand zelf, zonder vervangend lettertype.
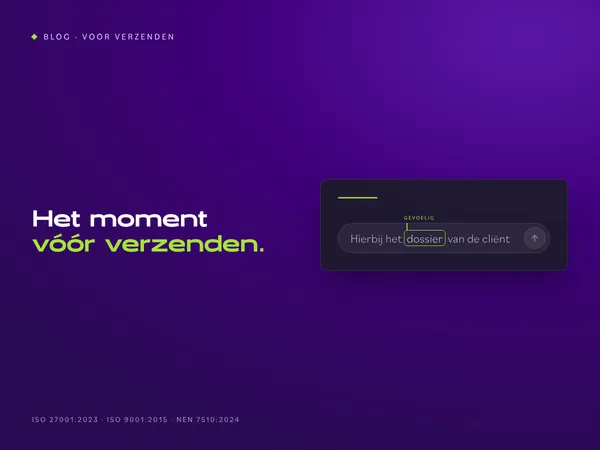
Inhoud: kicker “BLOG · VOOR VERZENDEN”, de kop in wit en limoengroen, en de chatkaart met “dossier” omlijnd en het label “gevoelig”. Er is geen maskering en er staan geen merknamen in.
Opmaak: de kop raakt de kaart niet en de certificeringsregel is volledig.
Randen: de hoekpixels zijn paars, niet de controlekleur 
#160a2e. Er is dus geen rand van de pagina mee geëxporteerd.

Het PNG-bestand gevoelige-gegevens-ai-chat-verzenden.png heb ik je gestuurd. Zet het in je Downloads en draai dan:

powershell
cd C:\repos\ALTA-ICT
git pull --rebase
$b = "docs\Projecten\social-campagnes\Week 43 - Voor Verzenden\Blog"
$f = Get-Item "$env:USERPROFILE\Downloads\gevoelige-gegevens-ai-chat-verzenden.png"
Add-Type -AssemblyName System.Drawing
$i = [System.Drawing.Image]::FromFile($f.FullName); "{0}x{1}" -f $i.Width, $i.Height; $i.Dispose()
Copy-Item $f.FullName "$b\" -Force
git add -- "$b\gevoelige-gegevens-ai-chat-verzenden.png"
git diff --cached --name-only
git commit -m "Blog 43: bloghero gevoelige gegevens voor verzenden"
git log origin/master..master --oneline

Verwachting: 1200x900, dan één bestandsnaam, daarna één of twee commits. Twee commits als de editie 15-hero nog niet gepusht is. Plak de output terug, daarna push je.

In WordPress, bij blog 43:

Uitgelichte afbeelding: upload dit bestand, met de alt-tekst uit de plakklaar.
Controleer na het uploaden dat de bestandsnaam geen -1 heeft gekregen.

De kanaalvarianten van blog 43 maak je pas als de blog live staat. De prompt staat in de plakklaar.

geef me blog 43 om te maken zoals het moet in wordpress

Hieronder staat alles voor WordPress, in de volgorde van de editor. Ik gebruik variant B, zonder test. Plak elke HTML in het tabblad Tekst en schakel nooit over naar Visueel.

1. Nieuw bericht
Ga naar Berichten, Nieuw bericht.

2. Titel

Gevoelige gegevens in AI-chat, Teams en WhatsApp: het moment vóór verzenden

3. Veld Introductie (tabblad Tekst)

html
<p dir="ltr">Bij een datalek denk je aan een hacker. In de praktijk begint het vaak met Ctrl+V: een stuk uit een dossier in de verkeerde chat, de verkeerde mail, of een AI-tool die de tekst "even netjes maakt".</p>
<p dir="ltr">Er is geen kwade wil. Er is haast, en een knop die te dichtbij zit. Deze blog gaat over dat ene moment vlak voor verzenden: wat kun je dan nog tegenhouden, en wie ziet het?</p>

4. Veld Omschrijving (tabblad Tekst)

html
<h2>Waar Microsoft 365 ophoudt</h2>
<p dir="ltr">In <a href="https://alta-ict.nl/blog/microsoft-purview-business-premium/">de blog over Microsoft Purview</a> zag je wat Business Premium al beschermt: mail en de bestanden in OneDrive en SharePoint. Een bestand dat je in Teams deelt, valt daar ook onder.</p>
<p dir="ltr">Het chatbericht in Teams niet. DLP voor Teams-chat vraagt volgens Microsoft een E5-licentie. En een AI-chat in de browser of een app op de laptop ziet Microsoft helemaal niet.</p>

<h2>AI-chat en geheimhouding</h2>
<p dir="ltr">Een medewerker plakt een brief aan een cliënt in een gratis AI-chat, met zijn privéaccount, om hem beter te formuleren. Naam, adres en de reden van het dossier gaan mee, naar een dienst waarmee je organisatie geen verwerkersovereenkomst heeft.</p>
<p dir="ltr">Verbieden werkt slecht. De tool blijft handig, en wie hem niet mag gebruiken, gebruikt hem stiekem. Beter: weten welke AI-tools je team gebruikt, en per tool afspreken wat erin mag.</p>

<h2>WhatsApp is geen dossier</h2>
<p dir="ltr">De wijkverpleegkundige stuurt een foto naar de collega die de dienst overneemt. De installateur appt de klant een offerte met diens adres. Het werkt snel, en het gebeurt vaak op een privételefoon.</p>
<p dir="ltr">Daarmee staan zakelijke gegevens op een apparaat dat de organisatie niet beheert, in een app die ze niet kan archiveren. Vertrekt de medewerker, dan vertrekken de gesprekken mee. Een alternatief moet net zo snel zijn, anders gebruikt niemand het.</p>

<h2>Een waarschuwing op het juiste moment</h2>
<p dir="ltr">Een training over datalekken vergeet je in een week. Een melding op het moment van verzenden niet. In Outlook kan Microsoft 365 dat al: staat er een gevoelig gegeven in een mail, dan verschijnt bovenaan een melding nog voor de mail vertrekt. Voor chat en voor apps buiten Microsoft heb je daarvoor software op het apparaat nodig.</p>

<h2>Beschermen zonder meekijken</h2>
<p dir="ltr">Elke vorm van datalekpreventie roept bij medewerkers en ondernemingsraad één vraag op: leest de werkgever mee? Stel die vraag zelf, vóór je iets kiest. Een melding per soort gegeven is genoeg om een lek te voorkomen. Namen en berichtinhoud zijn daarvoor niet nodig.</p>

<h2>Begin met een AI-overzicht</h2>
<p dir="ltr">Je hoeft niet met software te beginnen. Begin met een lijst van de AI-tools die je team gebruikt, waarvoor, en met welke gegevens. Vaak staan er tools op die niemand had verwacht.</p>
<p dir="ltr">De Europese AI-verordening legt de markering van AI-output bij de aanbieders. Sinds augustus moeten zij wat hun AI maakt machineleesbaar markeren; voor tools die al eerder op de markt waren, loopt de overgang tot 2 december. Dat is hun plicht. Jouw taak is weten wat je gebruikt.</p>
<p dir="ltr">Het <a href="https://airegister.alta-ict.nl/?utm_source=blog&amp;utm_medium=referral&amp;utm_campaign=voorverzenden&amp;utm_content=blog43-tool">AI-Register</a> geeft geen juridisch oordeel. Wel maakt het in ongeveer tien minuten een overzicht van je AI-tools met de transparantieteksten, als drie documenten in je mail.</p>

<h2>Zo doen wij het</h2>
<p dir="ltr">We beginnen met het AI-overzicht en de afspraken per tool. Daarna zetten we Purview aan voor mail en bestanden. Het gat buiten Microsoft vullen we met datalekpreventie op het apparaat, als add-on bij de moderne werkplek. We werken zelf onder ISO 27001:2023, ISO 9001:2015 en NEN 7510:2024.</p>

<h2>Veelgestelde vragen</h2>
<p dir="ltr"><strong>Mag een medewerker een AI-chat gebruiken voor werk?</strong></p>
<p dir="ltr">Dat bepaal je zelf, per tool. Leg vast welke tools mogen en welke gegevens er niet in horen. Een zakelijk abonnement met een verwerkersovereenkomst is iets anders dan een gratis versie met een privéaccount.</p>
<p dir="ltr"><strong>Beschermt Business Premium Teams?</strong></p>
<p dir="ltr">Bestanden die je in Teams deelt wel, want die staan in SharePoint of OneDrive. Het chatbericht zelf niet; daarvoor vraagt Microsoft E5.</p>
<p dir="ltr"><strong>Moet ik AI-output zelf markeren?</strong></p>
<p dir="ltr">De markering van AI-output is een plicht van de aanbieder van de AI-tool. Voor jou telt dat je weet welke tools je gebruikt en wat je erin stopt.</p>

<h2>Conclusie</h2>
<p dir="ltr">Het lek begint met plakken, niet met een hacker. Microsoft 365 beschermt mail en bestanden; de chat, de AI-tool en de app op de laptop vallen erbuiten. Begin met een overzicht van wat je team gebruikt en spreek per tool af wat erin mag.</p>
<p dir="ltr">Wil je het moment vóór verzenden bespreken? Plan een gesprek met ALTA-ICT.</p>

5. CTA-knop (als je thema een knopveld heeft)

Tekst: Het moment vóór verzenden bespreken
Link: https://alta-ict.nl/contact?utm_source=blog&utm_medium=referral&utm_campaign=voorverzenden&utm_content=blog43-cta

6. Uittreksel

Een datalek begint vaak niet bij een hacker, maar bij plakken. Wat er gebeurt als een medewerker gegevens in een AI-chat, een Teams-chat of WhatsApp zet, waar Microsoft 365 ophoudt, en waarom je begint met een overzicht van de AI die je team gebruikt.

7. Categorie: Beveiliging. Zet geen andere categorie aan.

8. Uitgelichte afbeelding

Upload gevoelige-gegevens-ai-chat-verzenden.png. Controleer daarna dat de bestandsnaam in de mediabibliotheek geen -1 heeft gekregen.
Alt-tekst:
Hero bij de blog over gevoelige gegevens vóór verzenden: een chatinvoerveld met de zin Hierbij het dossier van de cliënt, waarin het woord dossier omlijnd is en gemarkeerd als gevoelig.